4.8 on G2 | 4.8 on Capterra

Network Penetration Testing, Led by Human Testers

Red Sentry testers manually validate every finding across your external and internal networks, so you see what an attacker could actually reach, not a scanner export.

Human-led testing: Experienced testers exploit and confirm findings by hand, with tools used for discovery.

Reports that support your auditor: Evidence, severity, and remediation steps that support SOC 2, HIPAA, PCI DSS, and ISO 27001 reviews.

Retest included: After you fix, we retest and confirm each finding is closed.

Trusted by Companies That Can’t Afford Mistakes

1000+

Security assessments conducted

25,000+

Vulnerabilities discovered

4.8

on G2

4.8

on Capterra

Customer ratings
A methodology you can check.

Testing follows NIST SP 800-115.

Reconnaissance

Mapping your attack surface (subdomains, IPs, and active hosts).

Vulnerability Enumeration

Scanner-assisted discovery combined with manual analysis.

Manual Exploitation

The "Human Element." Our hackers safely exploit found vulnerabilities to prove business risk.

Reporting & Remediation

A prioritized list of findings with clear reproduction steps and a retest of your fixes.

External Network Pentest

External Network Pentest

The "Hacker's View"

We attack from the public internet to find open ports, weak firewalls, and exposed services.

Often requested for perimeter security and SOC 2 evidence.

Internal Network Pentest

Internal Network Pentest

The "Inside Threat"

We simulate a breach inside your firewall to test segmentation, lateral movement, and AD.

Often requested for PCI DSS, ISO 27001, and defense in depth.

Internal Network Pentest

The "Inside Threat"

We simulate a breach inside your firewall to test segmentation, lateral movement, and AD.

Often requested for PCI DSS, ISO 27001, and defense in depth.

Why Security Leaders Choose Red Sentry

for Network Penetration Testing

Jira integration that works - Findings become actionable tickets with CVEs and reproduction steps.

Reports for people and auditors - Executive dashboards, technical deep-dives, and CSV exports.

Evidence for your compliance reviews - Testing that supports SOC 2, HIPAA, PCI, DSS, and ISO 27001 reviews, scoped to your environment.

Manual validation, not scanner output - A finding is not reported until a tester confirms it.

Clear scoping - Scope and price are agreed before testing starts. Learn how scoping works.

Reports that support your compliance reviews

Every report includes evidence, severity, and remediation guidance that support SOC 2, HIPAA, PCI DSS, and ISO 27001 reviews, with evidence your auditor can review. See a sample report.
AICPA SOC badge
AICPA SOC badge

Red Sentry has completed a SOC 2 Type II examination.

Red Sentry has completed a SOC 2 Type II examination.

You're in Good Hands

  • “The Red Sentry team was able to deliver quick, but thorough, results for my business. Their responsiveness and findings were critical in closing a new client engagement. I am looking forward to working with them in the future.”

    Craig Serold | Partner

  • "Complete satisfaction. Nothing less. From concept to conclusion, you are in great hands throughout the entire process."

    Douglas G. | CEO

  • “Seamless, constructive, efficient. They are always quick to respond to customers and very easy to work with regarding scheduling.”

    Ryan M. | Director of Sales

  • “Very good. They provided recognized credibility and gave us a clean bill of health on issues we had resolved.”

    David N. | Leader of Client Delight

Powered by the Red Sentry PTaaS Platform

Powered by the Red Sentry PTaaS Platform

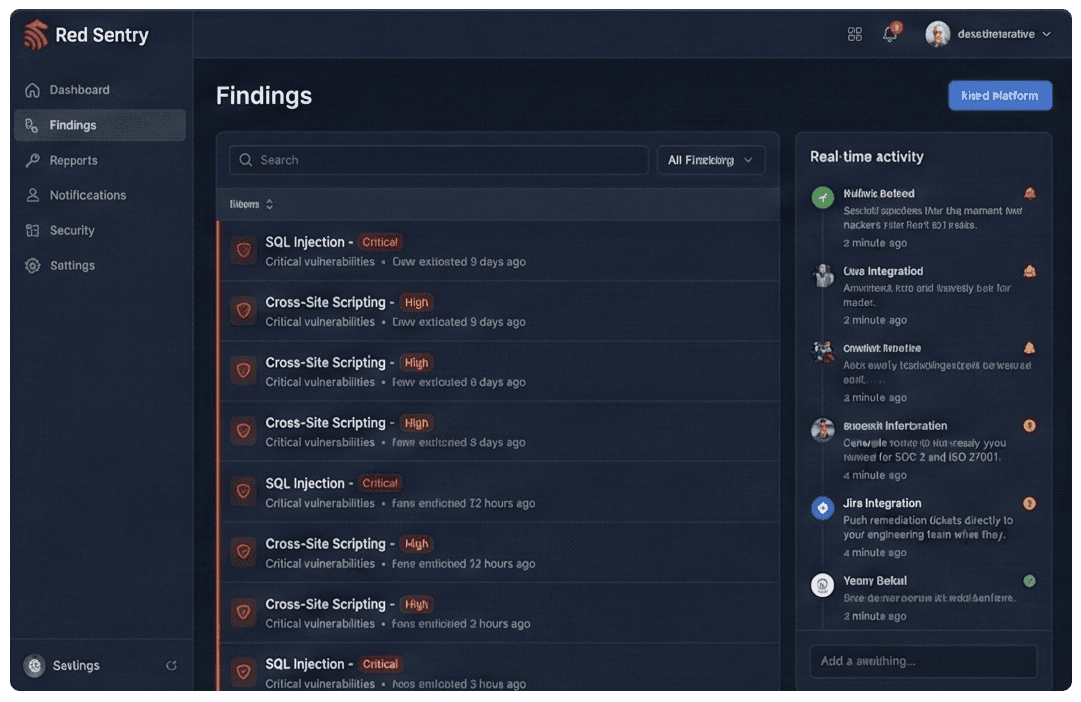
We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

How it works?

Scoping call

A security expert reviews your environment with you. We agree scope and send a proposal.

Testing is scheduled

Once scope is approved, we schedule testing with your team.

We test by hand

Human testers manually validate every finding. Confirmed findings appear in your Red Sentry portal.

Report and retest

You receive a report with evidence, severity, and remediation guidance, plus a retest of your fixes.
AICPA SOC badge
AICPA SOC badge

See how fast Network Pentesting can be. Book your complimentary scoping call today.

Frequently Asked Questions

Answers to the questions teams ask most when planning a network pentest. Need your applications tested too? See web application testing.

What is the difference between an external and an internal network pentest?

An external pentest tests your internet-facing systems, such as public IPs, domains, VPN endpoints, and exposed services. An internal pentest assumes an attacker is already inside your network and tests lateral movement, privilege escalation, segmentation, and Active Directory.

What do you need from us to scope a network pentest?

We ask about your external IPs and domains, your internal networks and locations, Active Directory, and any systems that need special handling. A security expert walks through it with you on the scoping call.

Will testing disrupt our systems?

We agree timing and rules of engagement with your team before testing starts, and testing is designed to minimize disruption.

Can a vulnerability scan replace a network pentest?

No. A scan gives you baseline visibility into known weaknesses. A pentest goes further: a tester manually validates findings, chains what is exploitable, and shows the real business impact.

Does a network pentest support SOC 2, PCI DSS, or ISO 27001?

Network pentesting is one of the technical tests these frameworks commonly call for, depending on your environment. We help you decide which tests fit, and the report gives your auditor technical evidence to review.

What is in the report?

Prioritized vulnerabilities with evidence, reproduction steps, remediation guidance, and a retest of your fixes.

How is pricing determined?

Pricing depends on the size and complexity of your environment and is set during the scoping call.

See how fast Network Pentesting can be. Book your complimentary scoping call today.

AICPA SOC badge
AICPA SOC badge

You're in Good Hands

  • “The Red Sentry team was able to deliver quick, but thorough, results for my business. Their responsiveness and findings were critical in closing a new client engagement. I am looking forward to working with them in the future.”

    Craig Serold | Partner

  • "Complete satisfaction. Nothing less. From concept to conclusion, you are in great hands throughout the entire process."

    Douglas G. | CEO

  • “Seamless, constructive, efficient. They are always quick to respond to customers and very easy to work with regarding scheduling.”

    Ryan M. | Director of Sales

  • “Very good. They provided recognized credibility and gave us a clean bill of health on issues we had resolved.”

    David N. | Leader of Client Delight