Rated 4.9/5 on G2 & Capterra

Rated 4.9/5 on G2 & Capterra

Internal Network Penetration Testing

Internal Network Penetration Testing

Firewalls aren't enough. We simulate an insider threat or compromised device to test your lateral movement defenses, internal segmentation, and Active Directory security.

Fill out the form to book a scoping call with a security expert. We’ll help define your requirements and pricing.

Trusted by Companies That Can’t Afford Mistakes

Trusted by Companies

That Can’t Afford Mistakes

The Assumed Breach:
Our Internal Methodology

The Assumed Breach:
Our Internal Methodology

We follow NIST SP 800-115 and PTES standards to ensure a rigorous, repeatable assessment.

We follow NIST SP 800-115 and PTES standards to ensure a rigorous, repeatable assessment.

PHASE 1

PHASE 2

PHASE 3

Access & Simulation

We start where the firewall ends. Connecting via a secure VPN or lightweight VM agent, we mimic a compromised employee laptop or a rogue device plugged into your office lobby.

Lateral Movement
We test your segmentation logic. Can a user on the Guest Wi-Fi access the Engineering database? We attempt to pivot across subnets to find paths to sensitive data.

Privilege Escalation

We target the 'Keys to the Kingdom.' Our hackers exploit misconfigured Active Directory settings and weak permissions to elevate access from a standard user to a Domain Admin.

PHASE 1

Access & Simulation

We start where the firewall ends. Connecting via a secure VPN or lightweight VM agent, we mimic a compromised employee laptop or a rogue device plugged into your office lobby.

PHASE 2

Lateral Movement
We test your segmentation logic. Can a user on the Guest Wi-Fi access the Engineering database? We attempt to pivot across subnets to find paths to sensitive data.

PHASE 3

Privilege Escalation

We target the 'Keys to the Kingdom.' Our hackers exploit misconfigured Active Directory settings and weak permissions to elevate access from a standard user to a Domain Admin.

The Process

The Process

WHAT WE TEST

Comprehensive Internal Coverage

Network Segmentation: Testing VLANs and subnet isolation.


Active Directory (AD): Identifying Kerberoasting, weak GPOs, and excessive admin rights.

Man-in-the-Middle (MitM): Intercepting unencrypted internal traffic.

Privilege Escalation: Attempting to gain Admin access from a low-level account.

Patch Management: Finding outdated software on internal servers.
What We Frequently Discover

LLMNR/NBT-NS Poisoning:

Stealing user credentials from broadcast traffic on the local network.

Default Credentials:

Printers, Routers, and IoT devices left with admin/admin.

Flat Networks:

No restrictions preventing a Guest user from accessing corporate servers.
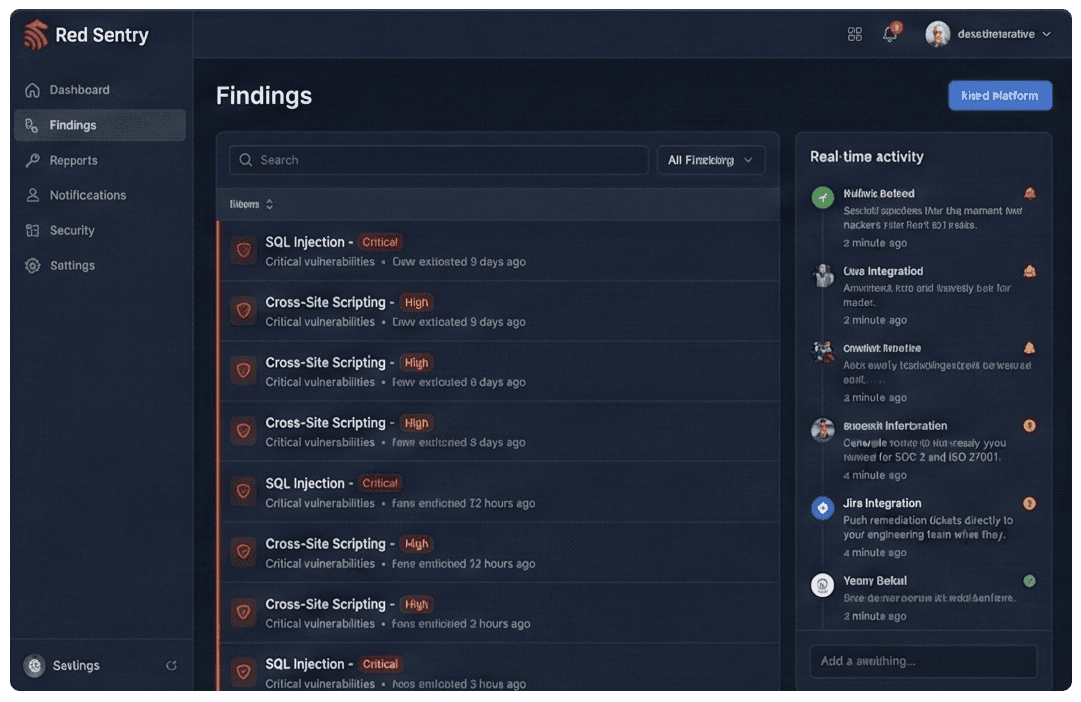
Powered by the Red Sentry PTaaS Platform

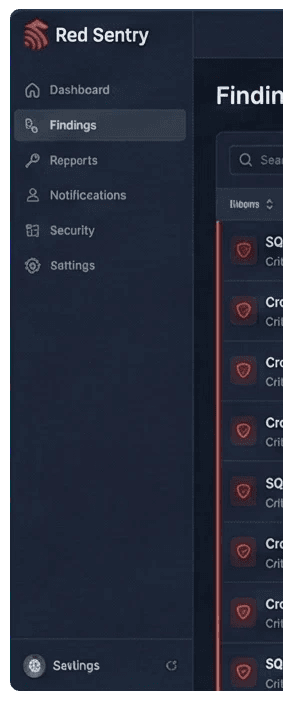
We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

One-Click Compliance: Generate the audit-ready reports you need for SOC 2 and ISO 27001 instantly.

Compliance-Ready Reports

Our reports map directly to the compliance frameworks SaaS companies need most — SOC 2, HIPAA, PCI, ISO 27001. Ready to drop straight into your auditor’s checklist.

Our reports map directly to the compliance frameworks SaaS companies need most — SOC 2, HIPAA, PCI, ISO 27001. Ready to drop straight into your auditor’s checklist.

Powered by the Red Sentry PTaaS Platform

We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

One-Click Compliance: Generate the audit-ready reports you need for SOC 2 and ISO 27001 instantly.

Stop Lateral Movement in Its Tracks.

Don't assume your firewall will catch everything. Validate your internal segmentation and prove to auditors that your sensitive data is unreachable—even if a breach occurs.

Perfect for SOC 2, ISO 27001, and HIPAA compliance.

Frequently Asked Questions

Frequently Asked Questions

How do you connect to our internal network remotely?

We make it incredibly simple. We don't need to fly a consultant to your office. We typically connect via a secure VPN profile you provide, or we can deploy a lightweight Virtual Machine (VM) or Docker container inside your environment. This acts as our "jump box," allowing our certified ethical hackers to assess your internal network securely from our SOC.

Will this testing trigger our internal security alarms?

Ideally, yes! One of the secondary goals of an internal pentest is to validate your "Blue Team" or SOC’s ability to detect an intrusion. However, we can adjust our "noise" level based on your goals. If you want a covert simulation to test your team's responsiveness, we will move quietly. If you want a comprehensive audit to find as many bugs as possible, we may trigger alerts, and we will coordinate with your IT team beforehand.

Do we need to whitelist your IP addresses?

This depends on the type of test you want. For a "Blackbox" (simulated attacker) approach, you would not whitelist us, forcing us to evade your defenses. However, for the most cost-effective and thorough results, we recommend a "Greybox" approach where you whitelist our testing appliance. This ensures our time is spent identifying deep vulnerabilities in your infrastructure rather than just fighting your firewall blocking rules.
Powered by the Red Sentry PTaaS Platform

We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

One-Click Compliance: Generate the audit-ready reports you need for SOC 2 and ISO 27001 instantly.

See how fast Internal Network Pentesting can be.

Fill out the form to book a scoping call with a security expert. We’ll help define your requirements and pricing.