Rated 4.9/5 on G2 & Capterra

Rated 4.9/5 on G2 & Capterra

External Network Penetration Testing

External Network Penetration Testing

Your perimeter is constantly changing. We combine continuous asset discovery with expert manual ethical hacking to secure your internet-facing infrastructure.

Fill out the form to book a scoping call with a security expert. We’ll help define your requirements and pricing.

Trusted by Companies That Can’t Afford Mistakes

Trusted by Companies

That Can’t Afford Mistakes

The Hacker’s Perspective: Our External Methodology

The Hacker’s Perspective: Our External Methodology

PHASE 1

PHASE 2

PHASE 3

OSINT & Reconnaissance

Before we scan, we hunt. We use Open Source Intelligence to find forgotten subdomains, exposed S3 buckets, and employee email dumps that attackers use to craft their entry.

Vulnerability Analysis
We identify misconfigured firewalls, outdated services (CVEs), and weak encryption protocols on all exposed IPs.

Manual

Exploitation

Our certified hackers attempt to bypass authentication, exploit logic flaws, and gain entry to your internal network from the outside.

PHASE 1

OSINT & Reconnaissance

Before we scan, we hunt. We use Open Source Intelligence to find forgotten subdomains, exposed S3 buckets, and employee email dumps that attackers use to craft their entry.

PHASE 2

Vulnerability Analysis
We identify misconfigured firewalls, outdated services (CVEs), and weak encryption protocols on all exposed IPs.

PHASE 3

Manual Exploitation

Our certified hackers attempt to bypass authentication, exploit logic flaws, and gain entry to your internal network from the outside.

The Process

The Process

WHAT WE TEST

Comprehensive Perimeter Coverage

Firewall Configurations: Testing for bypass methods and weak rules.

Open Ports & Services: Identifying unnecessary exposure to the public web.

Encryption Weaknesses: Finding outdated SSL/TLS protocols.

Authentication Portals: Testing specific login pages for brute-force risks.

DNS & Email Servers: Checking for spoofing risks and misconfigurations.

Note: This assessment covers your public-facing infrastructure (IPs/Domains). For deep internal cloud configuration (IAM, S3 policies), check out our Cloud Security Assessment.
What We Frequently Discover

Forgotten Dev Environments:

Staging servers left open to the public.

Weak VPN Gateways:

Outdated SSL VPNs vulnerable to brute force.

Exposed Databases:

MongoDB or Elasticsearch instances with no auth.
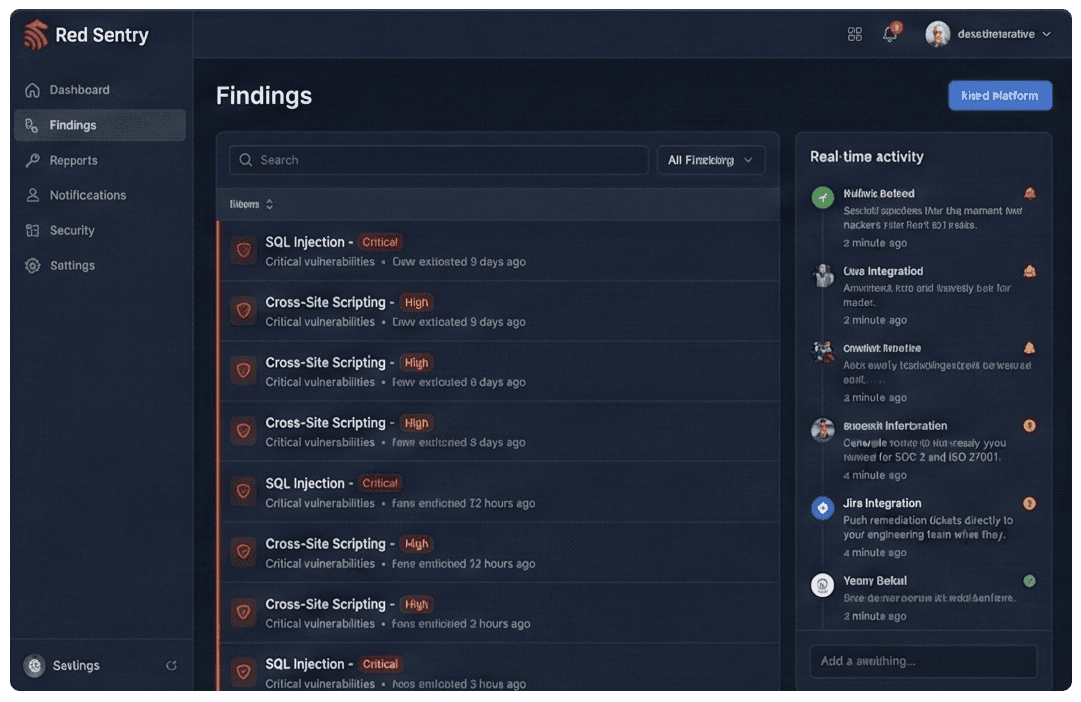
Powered by the Red Sentry PTaaS Platform

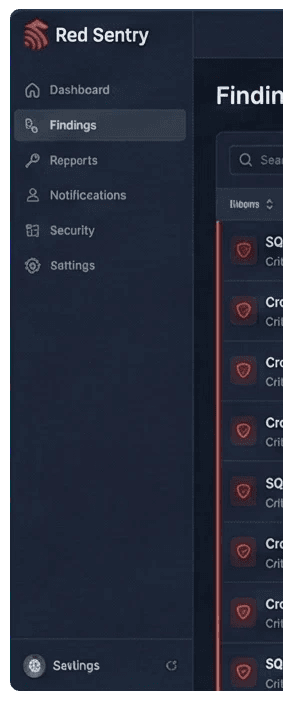
We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

One-Click Compliance: Generate the audit-ready reports you need for SOC 2 and ISO 27001 instantly.

Compliance-Ready Reports

Our reports map directly to the compliance frameworks SaaS companies need most — SOC 2, HIPAA, PCI, ISO 27001. Ready to drop straight into your auditor’s checklist.

Our reports map directly to the compliance frameworks SaaS companies need most — SOC 2, HIPAA, PCI, ISO 27001. Ready to drop straight into your auditor’s checklist.

Powered by the Red Sentry PTaaS Platform

We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

One-Click Compliance: Generate the audit-ready reports you need for SOC 2 and ISO 27001 instantly.

Lock Your Digital Doors Before Someone Checks the Handle

Hackers are scanning your perimeter every day. Beat them to the punch with a comprehensive external assessment that identifies open ports and exposed services in days, not weeks.

Includes free retesting for validated remediation.

Frequently Asked Questions

Frequently Asked Questions

Will this take down my website or interrupt our services?

No. Our primary goal is to identify vulnerabilities, not to disrupt your business. We do not perform Denial of Service (DoS) or Distributed Denial of Service (DDoS) attacks unless specifically requested as a stress test. We tune our scanning tools to be respectful of your bandwidth, and our manual pentesters exercise extreme caution when validating exploits to ensure your uptime is maintained.

How often should we run an External Network Pentest?

For compliance (SOC 2, ISO 27001), an annual pentest is the standard requirement. However, your external perimeter changes constantly—every time a developer spins up a new server or changes a firewall rule. Because of this, we recommend our Continuous Penetration Testing model, which monitors your external assets year-round, alerting you to new risks the moment they appear.

Do you check for leaked credentials on the Dark Web?

Yes. As part of the OSINT (Open Source Intelligence) phase of our external test, we scour public breaches, paste sites, and dark web repositories for compromised employee credentials. Attackers often use these leaked passwords to bypass your perimeter defenses (like VPNs or portals), so finding them before they do is a critical part of our methodology.

Do I need to provide you with IP addresses, or do you find them?

We can do both! In a Blackbox test, we start with just your company name and domain to see what we can find via OSINT. However, for the most comprehensive coverage, we recommend a Greybox approach where you provide a list of known IP ranges to ensure we don't miss assets you think are private but might be exposed.
Powered by the Red Sentry PTaaS Platform

We don’t just hand you a static PDF and walk away. Every single engagement includes full access to our Penetration Testing as a Service (PTaaS) platform at no extra cost. It’s the modern way to manage your security without the headaches of email threads and spreadsheets.

Real-Time Visibility: See critical risks the moment our hackers find them so you can start fixing immediately.

Jira Integration: Push remediation tickets directly to your engineering team where they actually work.

One-Click Compliance: Generate the audit-ready reports you need for SOC 2 and ISO 27001 instantly.

See how fast External Network Pentesting can be.

Fill out the form to book a scoping call with a security expert. We’ll help define your requirements and pricing.