Human-led testing: Experienced testers exploit and confirm findings by hand, with tools used for discovery.
Reports that support your auditor: Evidence, severity, and remediation steps that support SOC 2, HIPAA, PCI DSS, and ISO 27001 reviews.
Retest included: After you fix, we retest and confirm each finding is closed.
Not explicitly. The right testing depends on the environment, documented controls, risk, customer requirements, and auditor evidence expectations.
Auditors expect it. Control CC4.1 calls for ongoing evaluation that your security controls actually work, and a pentest is one of the clearest ways to show that.
Customers ask for it. It shows up on most vendor security questionnaires before a deal closes.
A pentest produces evidence either way, whether you are working toward a Type I report (controls designed correctly at a point in time) or a Type II report (controls operating effectively over a period, usually three to twelve months).
Good scope matches your actual environment, not a fixed package. Depending on what you run, that typically includes some combination of:
Web application testing (WAPT)
API testing
Cloud configuration review (AWS, Azure, GCP)
External network testing (ENPT)
Internal network testing (INPT)
Microsoft 365 / Google Workspace review, for organizations whose SOC 2 scope includes their identity and collaboration environment
We lock scope and pricing before testing starts, so there is no moving target once the engagement begins. For more on what a SOC 2 scope can include, read SOC 2 technical testing scope.
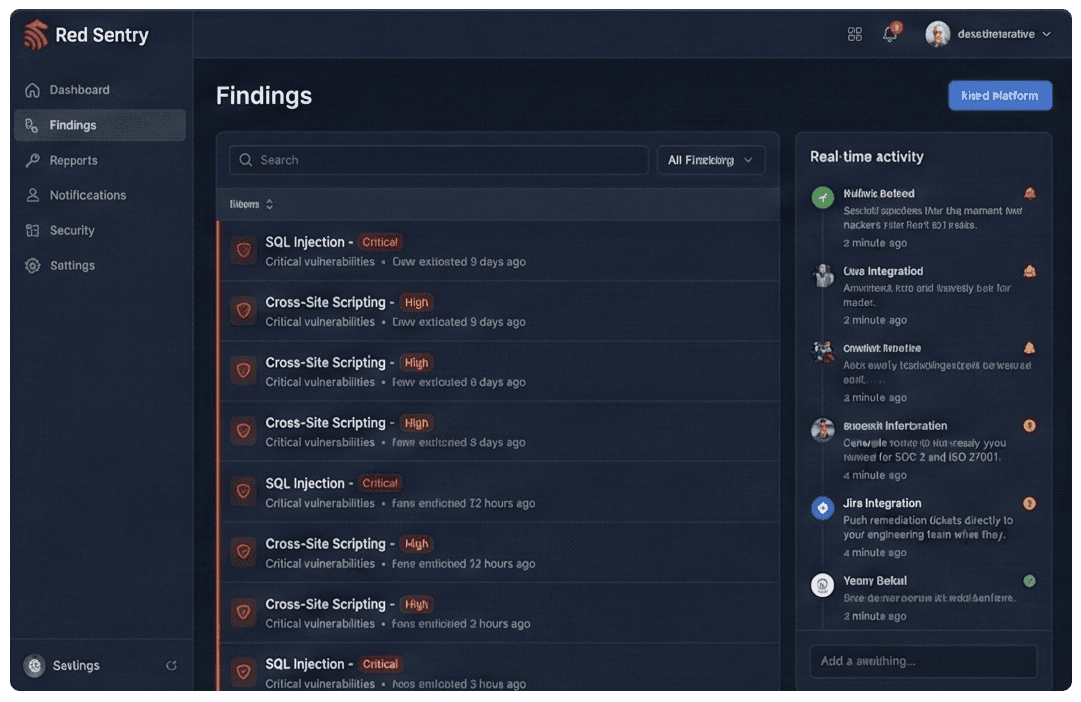
Tools help us find candidate issues fast. People decide what they mean. Reported findings are manually validated and exploitability is demonstrated where appropriate. That includes the things a scanner cannot reliably catch: chained exploits, business logic flaws, broken authentication, and multi-tenant isolation gaps.
Every engagement includes:
An executive summary and full technical report
Findings mapped to the relevant Trust Services Criteria
Reproducible steps your engineering team can act on
Prioritized remediation guidance
A Letter of Attestation, when your engagement calls for one
One complimentary retest to confirm fixes


“The Red Sentry team was able to deliver quick, but thorough, results for my business. Their responsiveness and findings were critical in closing a new client engagement. I am looking forward to working with them in the future.”
Craig Serold | Partner
"Complete satisfaction. Nothing less. From concept to conclusion, you are in great hands throughout the entire process."
Douglas G. | CEO
“Seamless, constructive, efficient. They are always quick to respond to customers and very easy to work with regarding scheduling.”
Ryan M. | Director of Sales
“Very good. They provided recognized credibility and gave us a clean bill of health on issues we had resolved.”
David N. | Leader of Client Delight

Does SOC 2 require a pentest?
Not by name. Control CC4.1 calls for ongoing evaluation that your security controls work, and most auditors and customers expect a pentest as evidence that they do.
Can a vulnerability scanner satisfy my auditor?
Rarely on its own. A scan gives you baseline visibility, but most auditors and customers expect the higher risk findings to be manually validated, which is what a pentest does.
What is included in the report?
An executive summary, full technical findings mapped to your Trust Services Criteria, reproducible steps, prioritized remediation guidance, a Letter of Attestation when applicable, and one complimentary retest.
How do you scope an engagement?
Scope follows your actual environment: web application, API, cloud, network, or whatever else is in play. We lock scope and pricing before testing starts.
What do your testers' credentials look like?
Our testers hold industry-recognized certifications such as OSCP, CISSP, CREST, and CCSP, plus additional credentials across offensive security, cloud security, and risk management. These are seasoned professionals, not junior analysts running tools behind the scenes.